2×4: eps2.2_init_1.asec
Episode Description: “elliot friends ray, hopes he can help finally delete mr. robot. dom makes a big discovery. darlene wonders whos the bigger threat – fbi or dark army?”
The .asec Filetype
The Android Secure Encrypted (.asec) filetype was created by Google to keep existing Android apps immutable so they can’t be changed or corrupted. Decrypted .asec files are converted back to the Android Package (APK) file format.
Elliot using uTorrent v3.2.1 to Watch a Movie with Darlene
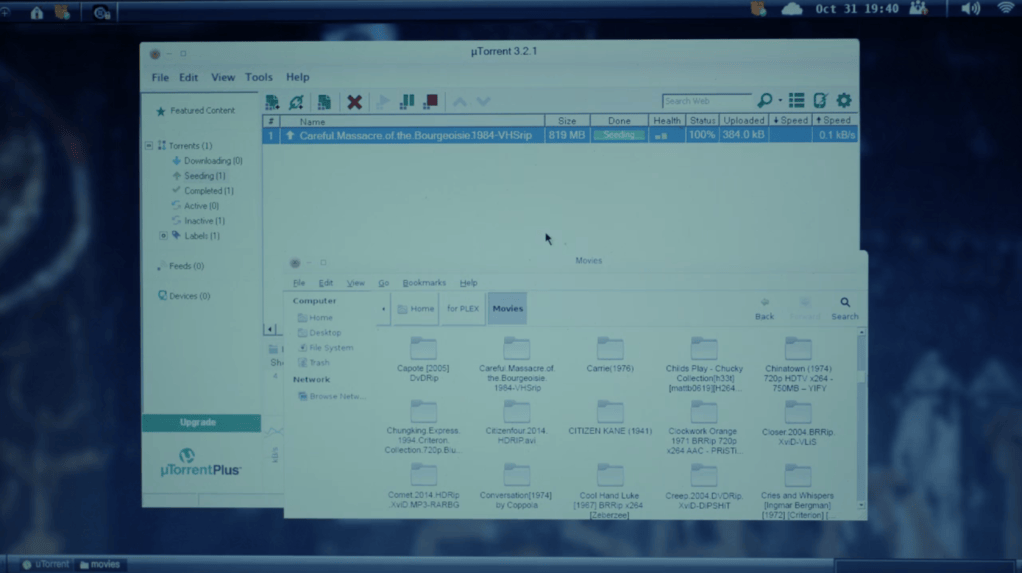
The episode starts with Darlene stopping by Elliot’s apartment in a flashback and using a code word that’s a reference to Linux/Unix computers (“init 1”) to show that she’s in distress and needs to spend time with him that night. They watch a movie from their childhood titled “The Careful Massacre of the Bourgoise” that’s a VHS rip in MP4 format from multiple folders Elliot has within a uTorrent window. Of course Elliot would pirate movies.
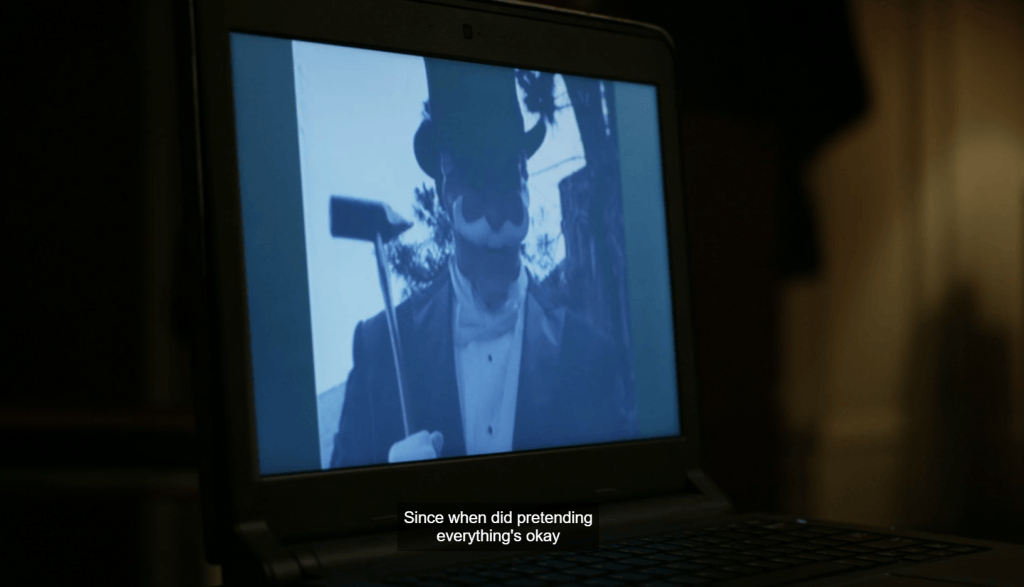
More importantly, this movie (which was created for the show and doesn’t actually exist) is a means to show how the two siblings thought of the “Mr.Robot” persona and mask for their movement later in life. It’s basically a story about a New Year’s party attended by a bunch of rich kids who get stalked and murdered by the killer dressed exactly like Mr.Robot in their fsociety broadcasts.
Darlene’s PostMates Hack for Affiliate Rewards
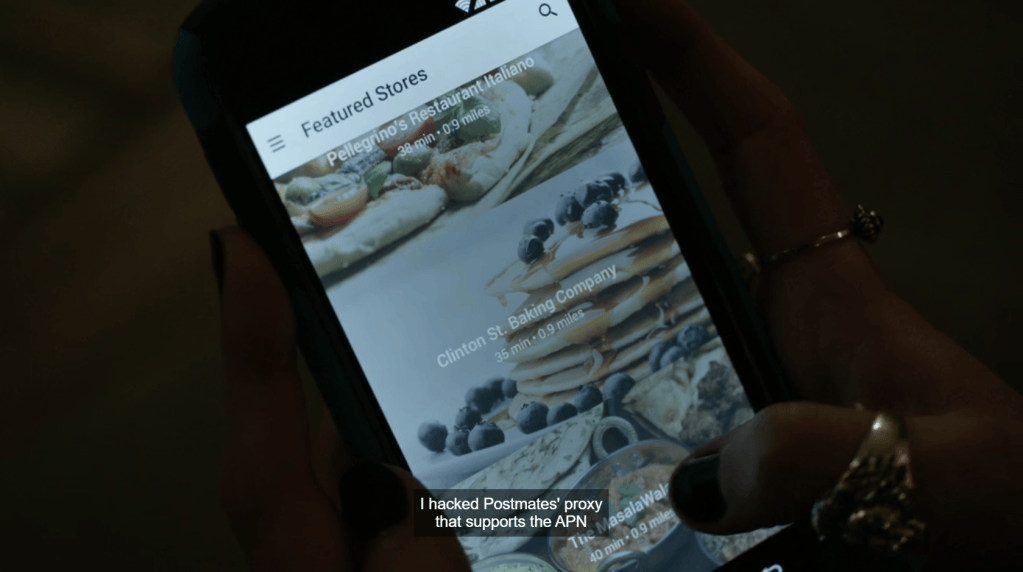
While ordering food during her movie night with Elliot, Darlene mentions that she hacked the proxy used by PostMates to support her boyfriend’s cell carrier’s Access Point Name (APN) so that any requests to PostMates’ website do a URL rewrite to her affiliate link and she gets the $10 coupon reward from it as if she referred those people to the service herself.
To start, APNs are the gateway between mobile carrier networks and other networks like the public Internet. This means that it would be the point where all requests to access the Internet from people’s phones would have to go through for the specific Mobile Service Provider (lets say Verizon for this example). So Darlene would be receiving affiliate rewards from what would have been thousands of people. Seeing a user account receiving this many coupons should have been an obvious tell to anyone handling PostMates’ backend that something wasn’t right, but in 2012 or whenever this flashback took place that could’ve easily been overlooked.
2×5: eps2.3_logic-b0mb.hc
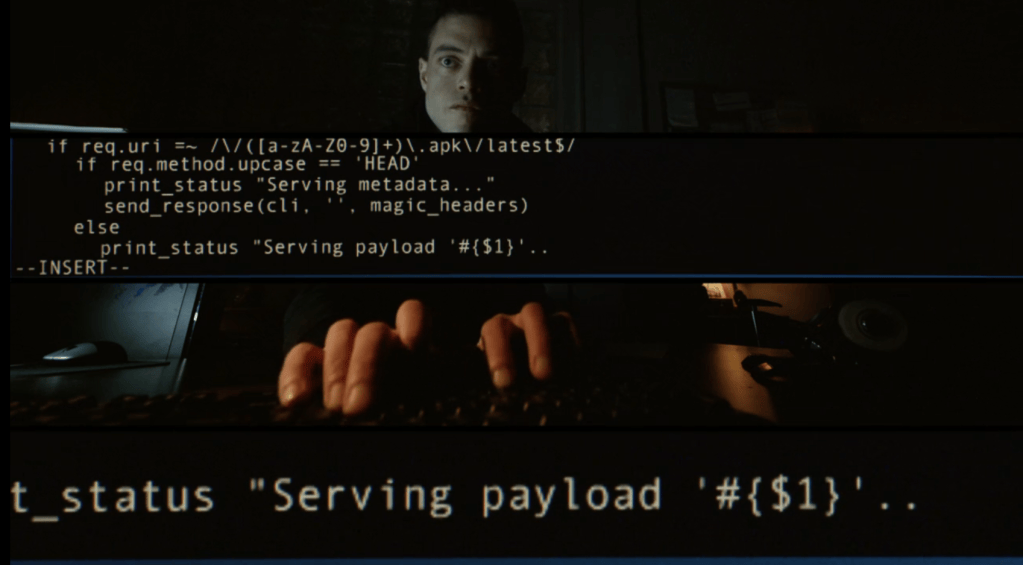
Episode Description: “elliot cant quit the game but tbh it proves bigger than expected. dom and fbi go to china to investigate five/nine. joanna is haunted – or hunted? darlene calls on angela for help.”
The .hc Filetype
The .hc file extension is for the VeraCrypt open-source encryption application. It’s a fork of TrueCrypt which was referenced with the .tc file extensions in the first and second episode titles of this season.
Elliot’s Android Phone Hack on the FBI
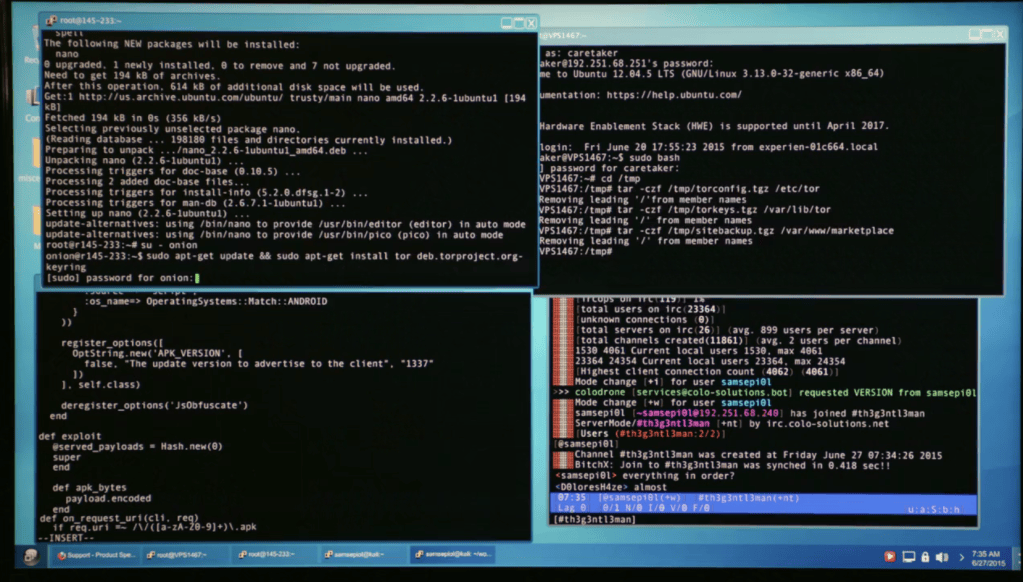
At the end of the previous episode we see Elliot connecting to a Kali Linux server using PuTTY and looking up an article on the FBI switching from Blackberries to Android phones for their staff, which segues into the beginning of this episode with Elliot setting up an Android hack in Metasploit to get access to the agents’ phones to see what they know about fsociety.
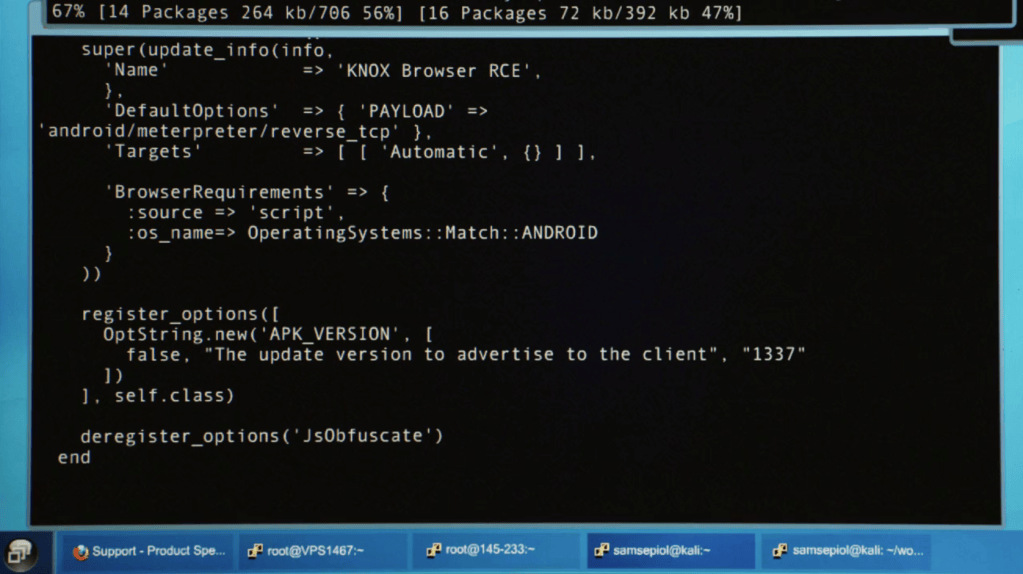
Elliot’s hack relies upon a Metasploit module named “Knox Browser RCE” (which in real life was named ‘Samsung Galaxy KNOX Android Browser RCE’ but they probably took the Samsung stuff out to avoid issues with the company).
The entire thing can be read here: https://github.com/rapid7/metasploit-framework/blob/master/modules/exploits/android/browser/samsung_knox_smdm_url.rb It even lists “Elliot Alderson” as one of the authors for a fun little easter egg.
Here’s the description given for the module:
“A vulnerability exists in the KNOX security component of the Samsung Galaxy firmware that allows a remote webpage to install an APK with arbitrary permissions by abusing the ‘smdm://’ protocol handler registered by the KNOX component.
The vulnerability has been confirmed in the Samsung Galaxy S4, S5, Note 3,and Ace 4.“
There’s a great breakdown of the vulnerability at this Quarks Lab page referenced in the module: https://blog.quarkslab.com/abusing-samsung-knox-to-remotely-install-a-malicious-application-story-of-a-half-patched-vulnerability.html
Basically the Mobile Device Management (MDM) application installed by default on the Read-Only Memory of specific Samsung phones and tablets (included as part of the KNOX enterprise security solution Samsung offered at the time) was vulnerable to being tricked by a malicious remote webpage visited by the user to install any Android Package Kit (APK) file the attacker wanted.
Basically, with phishing via e-mail or browser access to a link to the malicious webpage, attackers could install any app they wanted on the phone with full root level permissions. All the victim would see is a pop-up on their phone or tablet asking the user if they want to update, and because it was a trusted application asking (the enterprise MDM solution) most users would just accept.
2×6: eps2.4_m4ster-s1ave.aes
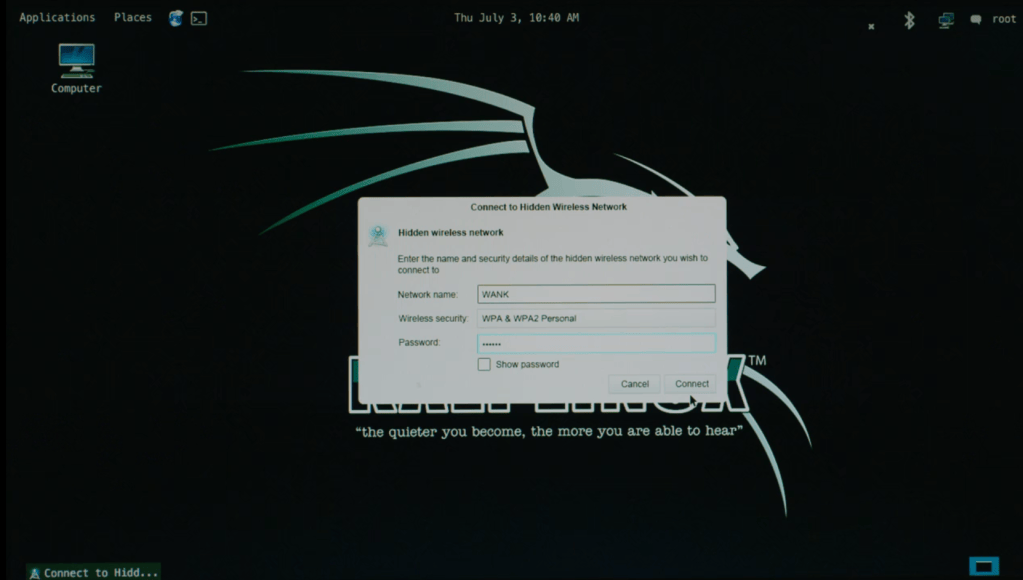
Description: “mr. robot attempts to show elliot that he can be useful. darlene and angelas plan doesnt go as expected.”
fsociety Sets up a Femtocell for Hacking FBI Cell Phones
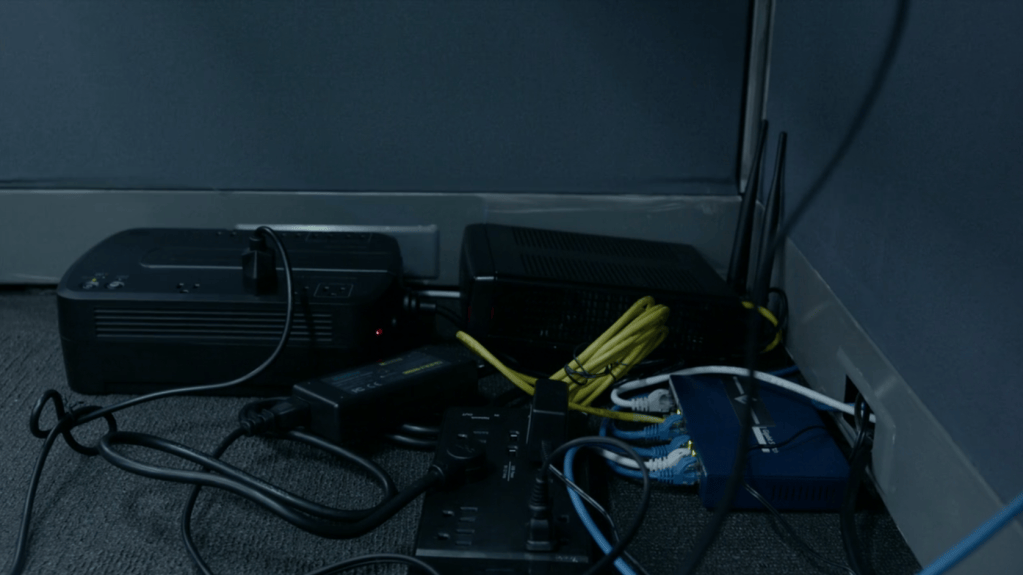
In order to “pwn” the FBI’s employee smartphones, the fsociety crew have Angela plant a femtocell (basically a small cell provider radio tower like the ones your phone regularly connects to) in the Evil Corp building on the floor where the FBI agents have set up shop for their investigation.
Angela goes to a part of the office on the FBI’s sequestered floor that seems unoccupied, and dips under a cubicle to plant a UPS and femtocell that she then plugs into a network switch. The femtocell’s been flashed with modified firmware, giving fsociety and The Dark Army an easy way into Evil Corp’s network which the FBI agents are currently on.
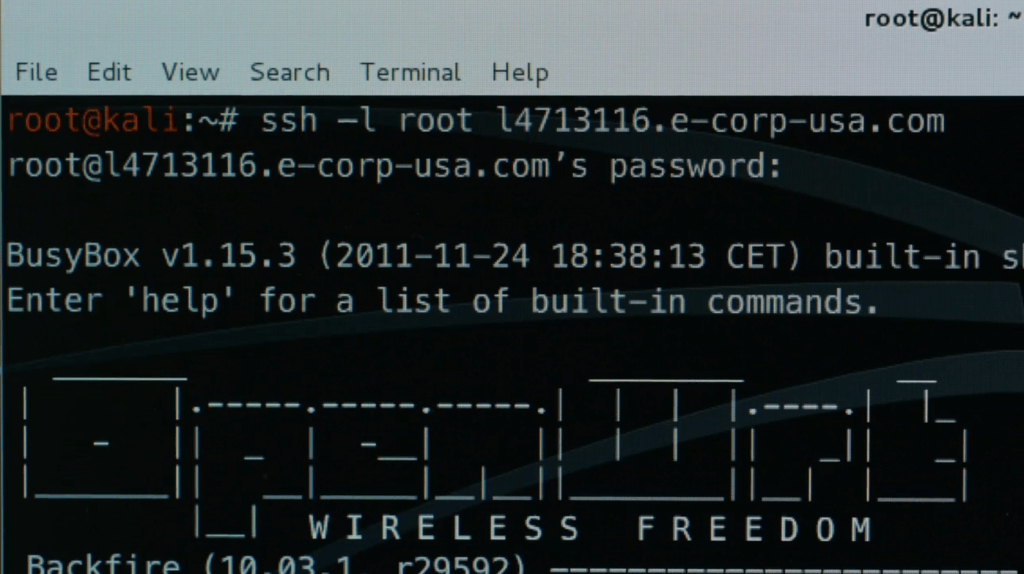
Angela gets back to her desk so she can SSH into the femtocell and use ifconfig to configure its WLAN connections to allow fsociety into the device (and by extension the network). It’s a nerve wracking scene where she’s looking over her shoulder and feeling a level of tension that’s more appropriate for bomb defusing than working on a terminal.
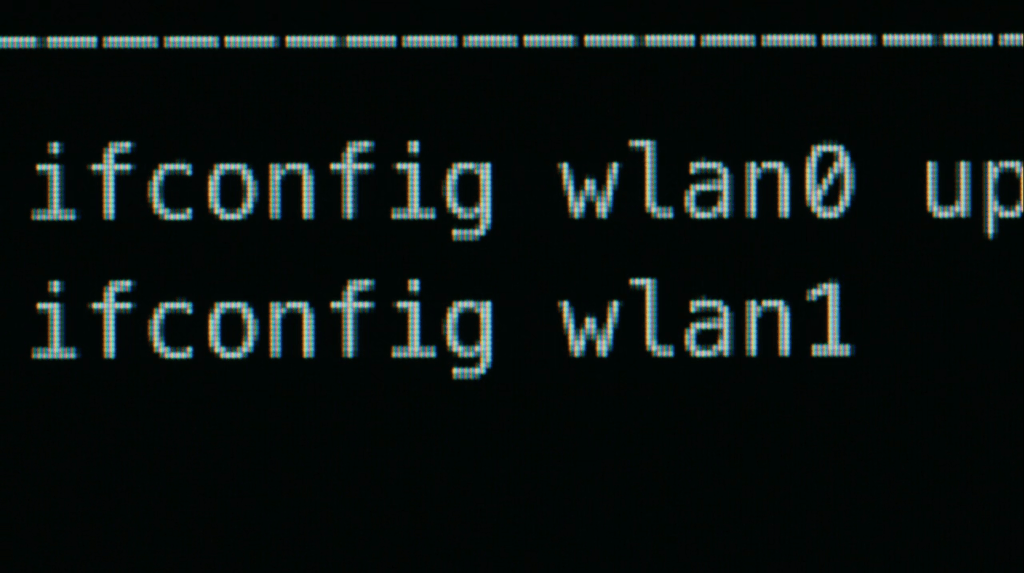
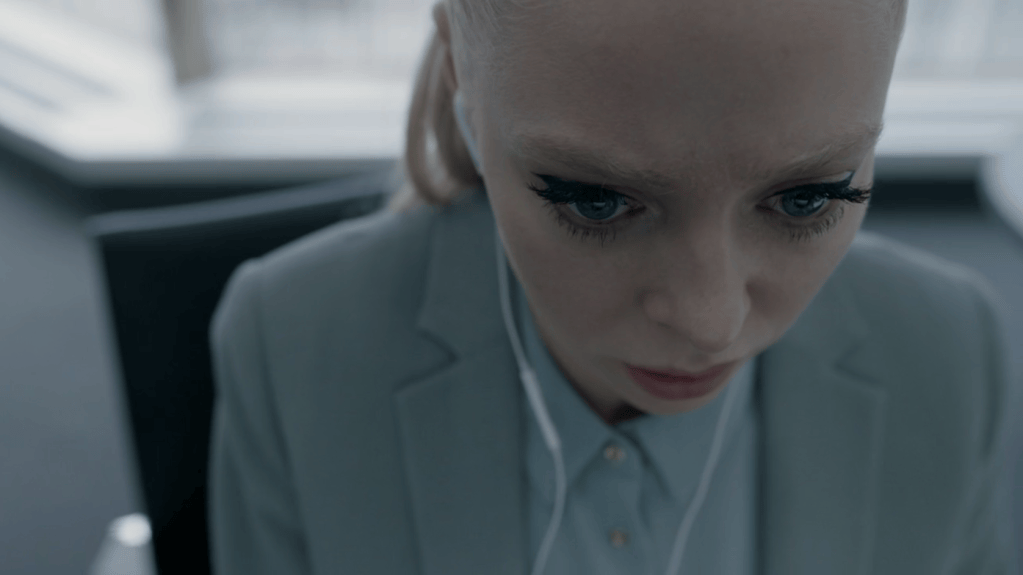
To be fair to the character and the scene, she is committing a felony that could also be argued to be treason since she’s aiding a Chinese hacker gang with ties to the PRC (The Dark Army) and their partners in accessing FBI data. With that being considered, it makes sense that Angela’s damn near about to pee her pants (or skirt) from the tension.
In Conclusion
These episodes have really raised the quality of the hacking material in the show. I’ve always appreciated shows that include shots of code and commands that are actually coherent. With having the show on streaming, it’s a fun little activity to pause the episode and read through what’s being typed out. It’s amazing to be able to review the code for the Metasploit module that “Elliot” wrote and the great write-up of how the exploit actually works from Quark Labs. 10/10, would read again.


Sound off in the comments about anything InfoSec or InfoTech.